DPDP Compliance Solution: A Practical Guide for Businesses in India
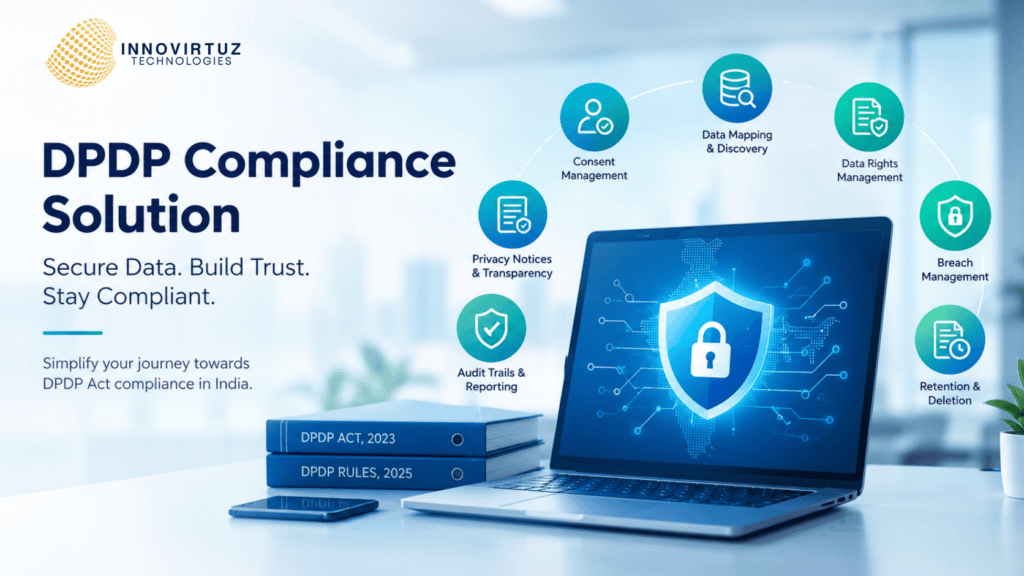
DPDP Compliance Solution: A Practical Guide for Businesses in India Businesses today collect and process personal data at almost every digital touchpoint—from websites and mobile applications to customer onboarding, employee systems, CRM platforms, cloud applications, and connected devices. As the volume of digital personal data grows, organisations need stronger processes to understand how data is collected, used, stored, shared, and deleted. In India, the Digital Personal Data Protection Act, 2023 (DPDP Act) establishes a legal framework for processing digital personal data while recognising individuals’ rights and organisations’ need to process data for lawful purposes. The Government subsequently notified the Digital Personal Data Protection Rules, 2025, providing the implementation framework for the Act. This is where a DPDP compliance solution can help organisations turn privacy requirements into practical, repeatable processes. What Is a DPDP Compliance Solution? A DPDP compliance solution is a combination of technology, processes, controls, and governance practices designed to help an organisation operationalise its obligations under India’s data protection framework. It can help organisations manage activities such as: Personal data discovery and mapping Consent collection and management Privacy notices Consent withdrawal Data Principal rights requests Data retention and deletion Data breach workflows Audit trails and compliance evidence Vendor and Data Processor governance Privacy risk assessment Compliance monitoring Importantly, the DPDP framework does not simply require an organisation to purchase a particular software product. The organisation remains responsible for establishing appropriate processes and controls. Technology can help automate and manage these activities at scale. Why Is DPDP Compliance Important for Businesses? For many organisations, personal data is distributed across multiple systems and departments. Marketing may collect customer information through websites, sales teams may use CRM platforms, HR may manage employee records, and IT teams may maintain databases and cloud infrastructure. Without proper governance, organisations can struggle to answer basic questions: What personal data do we collect? Why do we collect it? Where is it stored? Who can access it? Which third parties process it? How is consent recorded? How can an individual withdraw consent? When should personal data be deleted? What happens when a data breach occurs? A structured DPDP compliance programme helps bring these activities under a defined governance framework. The DPDP Rules, 2025 also place emphasis on clear and understandable notices, including information about the personal data being processed and the purpose of processing. They also provide mechanisms relating to consent withdrawal, exercising rights, and complaints. Key Components of a DPDP Compliance Solution 1. Personal Data Discovery and Mapping The first step is understanding what personal data exists within the organisation. A compliance solution can help identify data across databases, applications, cloud environments, websites, mobile applications, HR systems, CRM platforms, and other business systems. Data mapping can provide visibility into: What personal data is collected The purpose of processing Where data is stored How data moves between systems Which teams access the data Which third-party Data Processors handle it This visibility creates a foundation for effective privacy governance. 2. Consent Management Consent is an important part of the DPDP framework where consent is the applicable legal basis for processing. A technology-enabled consent management system can help organisations capture, record, track, update, and manage consent across different digital touchpoints. It can also help maintain records that demonstrate what an individual consented to and when. The DPDP Rules, 2025 emphasise clear, standalone, understandable notices and provide for mechanisms through which Data Principals can withdraw consent and exercise their rights. 3. Data Principal Rights Management The DPDP framework provides rights to individuals, referred to as Data Principals. Organisations therefore need processes to receive, verify, track, and respond to applicable requests. A DPDP compliance solution can provide a central workflow for managing these requests instead of relying on scattered emails, spreadsheets, or manual follow-ups. This can improve accountability and make it easier for privacy teams to track request status and supporting evidence. 4. Data Retention and Deletion Collecting personal data is only one part of data governance. Organisations also need to understand how long data should be retained and when it should be removed, subject to applicable legal and business requirements. A compliance solution can connect retention policies with operational systems and create workflows for data deletion or review. Automating these processes can reduce the risk of retaining personal information longer than necessary. 5. Data Breach Management Data security is a critical component of privacy compliance. Organisations need appropriate technical and organisational measures to protect personal data and processes for responding to incidents. A DPDP compliance solution can support: Incident reporting Internal escalation Breach response workflows Evidence collection Notification processes Incident tracking Post-incident review A centralised workflow can help organisations respond consistently rather than building a response process from scratch during an incident. 6. Audit Trails and Compliance Evidence One of the challenges of privacy management is demonstrating what an organisation actually did. A good compliance solution should maintain appropriate records of activities such as consent events, policy changes, rights requests, data processing activities, and compliance actions. These records can help privacy, legal, security, and management teams understand the organisation’s compliance position and identify gaps. How to Implement DPDP Compliance in India A practical implementation approach can be divided into several stages. Step 1: Identify Personal Data Create an inventory of the personal data your organisation collects and processes. Step 2: Map Data Flows Document where data comes from, where it goes, how it is processed, and which third parties have access to it. Step 3: Identify Compliance Gaps Compare existing practices, systems, policies, contracts, and processes against applicable DPDP requirements. Step 4: Establish Privacy Controls Implement appropriate consent, notice, access, retention, deletion, security, and rights-management processes. Step 5: Automate Where Practical Use compliance technology to reduce manual work and create consistent workflows across systems. Step 6: Monitor and Improve DPDP compliance should be treated as an ongoing operational programme rather than a one-time documentation exercise. What Should You Look for in a DPDP Compliance Solution? Before selecting a solution, organisations should evaluate whether it can support their